

By Gaurav Mohan, VP Sales SAARC & Middle East, NETSCOUT
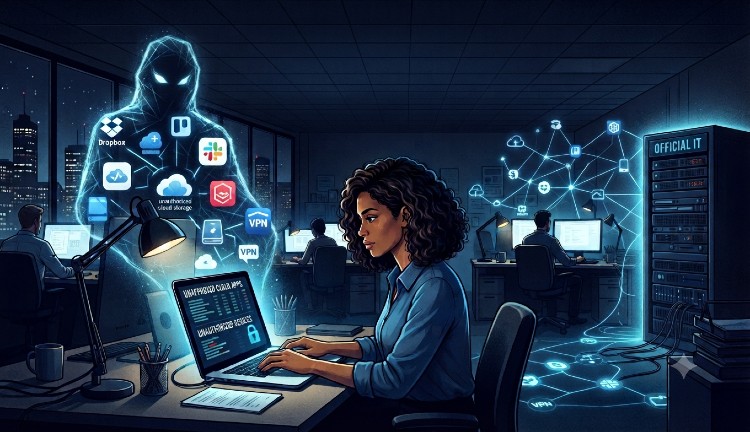
Shadow IT emerged from the tension between speed and formal processes when employees started to use unapproved hardware and software to work faster. Enterprises responded with procurement discipline, endpoint controls, and identity governance, establishing a workable balance between innovation and oversight.
Shadow AI introduces a new leadership risk with AI-assisted decisions getting woven into everyday workflows, often overtaking visibility and accountability. More than a failure of policy, it reflects a structural shift in how work is executed and decisions are made at scale. Embedded AI can create hidden dependencies, data leakage, and performance risks within approved platforms, making it a challenge to identify its influence. With AI operating at machine speed and governance moving at human pace, risk can accumulate quietly, limiting leadership’s ability to act decisively or explain outcomes when it matters most.
Why Shadow AI Challenges Traditional Shadow IT Assumptions
The defining risk of Shadow AI is not adoption per se, but the timing. Unlike traditional Shadow IT, AI operates continuously across workflows, making decisions and forming dependencies before governance can respond. Even approved platforms where AI operates within can produce outcomes that governance was never designed to monitor in real time.
This velocity can obscure the source of performance issues, weaken accountability, and make outcomes harder for leaders to trace and explain. For example, an AI-enabled customer service platform may experience latency caused by an external API, yet teams may struggle to determine whether the problem lies with the application, infrastructure, or AI provider. Leadership is then left answering for performance without clear, independent evidence of where the problem began.
How Shadow AI spreads and blind spots that matter
Shadow AI is integrating into everyday workflows, creating operational dependencies before leadership has reason to intervene. External services, AI features within approved platforms, and automations often remain active and interconnected, with limited visibility. Over time, these dependencies become difficult for leadership to inventory or unwind.
Yet many governance models still depend on inventory, disclosure, and periodic reviews. By the time these mechanisms engage, Shadow AI may already be entrenched, leaving leadership to manage risk reactively, with lots of uncertainty, rather than with foresight and knowledge. When leaders have to make decisions with incomplete context, or without a clear view of dependencies, there is the real risk of Shadow AI doing more damage unintentionally, than goodness, intentionally. Regulated data could be unknowingly exposed through AI prompts by employees.
AI-generated content can make social engineering attempts harder to distinguish from routine communications. In the absence of behavioral context, harmful activity looks legitimate, with governance blind spots staying alongside these challenges. Organizations cannot demonstrate how AI is actually being used or whether guardrails were enforced. As a result, leadership manages impact without timely proof of what happened or why.
Rethinking How to Manage and Monitor Shadow AI
Traditional monitoring was designed for post-adoption review, not real-time behavioral governance. Identity, endpoint, and application tools generate accurate signals, but often lack continuity across systems and time, leaving leaders with fragmented context when they need to understand and explain outcomes. Governing Shadow AI therefore requires behavioral evidence, not solely deeper inspection.
Modern monitoring in the agentic era must provide continuous visibility into how AI services and agents interact across the network, including destination patterns, interaction frequency, traffic characteristics, and how services perform under load. Even when payloads are encrypted, behavioral patterns can reveal new AI dependencies, performance degradation, or runaway agent activity before they escalate into business-impacting incidents.
Mapping these dependencies across AI services, SaaS platforms, and network paths changes the performance conversation and strengthens incident response. Vendor-independent, unimpeachable network evidence can establish when an AI service emerged, what systems it influenced, and how it behaved over time. This layer of monitoring is independent of vendor instrumentation and remains effective as AI tools, models, and platforms evolve. In a landscape defined by constant change, durability is key because executives require oversight that sustains clarity eventually, instead of insight that degrades as platforms evolve.
Governing Shadow AI with Confidence
The instinctive response to Shadow AI is often to restrict it, more importantly at the leadership level, but this approach may not succeed. But AI adoption represents a lasting shift in how work gets done, not a temporary trend that can simply be managed. The governance question is therefore changing, from deciding which AI solutions are permitted to whether leaders can see, understand, and explain AI-driven activity as it unfolds.
This makes monitoring a foundation for responsible progress, not a constraint on innovation. Shadow IT was primarily a visibility challenge, but Shadow AI makes it a leadership challenge, as timelines compress, exposure expands, and the cost of uncertainty rises. In this environment, visibility enables judgment, and without it, leadership operates on assumptions. On the other hand, with visibility, organizations can act decisively and defend their decisions with evidence.
Organizations that use network-level monitoring to identify emerging AI service patterns can reduce blind spots without slowing adoption or innovation. By understanding what happened, when it happened, and why, leaders can strengthen performance, resilience, and accountability while allowing AI to continue evolving across the enterprise.