Governance is the operating system for responsible AI at scale: Nitin Mehta, EY India


For years, enterprise technology governance has been built around systems that behave largely as they are programmed to behave. Controls could be designed around applications, data, access privileges and predictable decision paths. Artificial intelligence is fundamentally disrupting that model.
As Indian enterprises move from generative AI experimentation to AI-enabled workflows and increasingly towards agentic systems capable of accessing data, calling tools and taking actions- the governance question is no longer simply whether an AI model can be trusted. It is whether the AI system can be trusted to act on the organisation’s behalf.
This is creating a new governance challenge for banks, insurers, GCCs, digital platforms and large enterprises. Existing disciplines around software development, model validation, data governance and cybersecurity remain essential, but they were not designed for systems that can generate, reason, adapt and increasingly act.
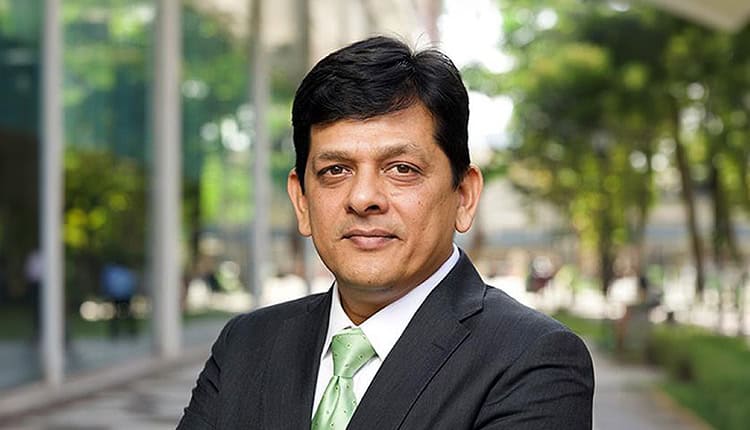
According to Nitin Mehta, Digital Risk Leader, EY India, enterprises now need to rethink AI governance as an end-to-end discipline spanning the entire AI value chain — from data and models to prompts, agents, tool access, human oversight, decisions and outcomes.
“Many Indian and global enterprises still govern AI using controls designed for an earlier technology era,” Mehta says. “A modern enterprise AI governance framework must cover the entire AI value chain: data, models, prompts, agents, tool access, human oversight, decisions and outcomes.”
The implication is significant. AI governance can no longer remain a policy document or a compliance checkpoint at the end of the development cycle. It needs to become part of the architecture through which AI is built, deployed, monitored and ultimately retired.
The governance question is moving from models to machines that act
The rise of agentic AI makes this shift particularly urgent.
A traditional AI governance conversation might ask whether a model produces accurate, fair and explainable outputs. An autonomous AI system introduces an additional question: what happens after the model produces the output?
An agent can access enterprise information, interact with applications, call tools, trigger workflows and potentially make decisions with real-world consequences.
“Agentic AI raises the governance bar for Indian enterprises,” Mehta says. “Leaders must move beyond asking whether an AI model produces a reliable answer and consider whether an AI-enabled system should be permitted to act on the organisation’s behalf.”
That means organisations need explicit boundaries around autonomy. They must determine what an agent can do independently, which actions require human approval and what activities should never be automated.
Permissions, too, need to be treated differently. Mehta argues that agent access should follow privileged-access principles, including least privilege, segregation of duties, transaction limits, time-bound access and periodic reviews.
But control cannot stop at access.
“For CXOs, explainability must extend beyond model outputs to agent actions: why a particular tool was selected, why specific data was accessed and why a workflow was triggered,” he says.
Every agent, therefore, needs a named owner, defined operating boundaries, an audit trail, continuous monitoring, an escalation mechanism and an effective kill switch.
The objective is not to prevent autonomy but to make autonomy accountable.
Governance needs to become an engineering discipline
This is where Mehta sees another fundamental transformation taking place: AI governance itself must become an engineering discipline.
Policy is necessary, but policy alone cannot create trusted AI at enterprise scale.
“AI governance must become an engineering discipline,” he says.
For Indian enterprises, particularly those with large technology teams, GCCs and multiple business units developing AI solutions, governance needs to be embedded across the lifecycle — from ideation and development through deployment, monitoring and retirement.
Every AI use case should enter a governed pipeline that captures its business owner, intended purpose, risk classification, data lineage, privacy and security considerations, testing evidence, approval status and monitoring requirements.
The control architecture needs to be equally comprehensive.
Mehta advocates a centralised inventory covering models, prompts, agents and third-party AI services, supported by automated risk scoring, role-based access controls and traceability across data, model versions and deployment environments.
Audit trails should capture changes to models, prompts and agents, while continuous testing should assess accuracy, bias, drift, resilience, hallucinations and security vulnerabilities.
The larger point is that governance should not be treated as an additional approval layer.
“When designed well, governance reduces rather than adds friction,” Mehta says. “It gives teams a clear control pathway and enables faster execution within defined risk boundaries.”
The board needs an AI risk map, not an AI strategy slide
This transformation also changes the conversation at the board level.
As boards increasingly approve AI investments and transformation programmes, Mehta believes they need visibility into something that many organisations are yet to fully map: their AI risk surface.
Every large enterprise, he argues, should maintain an AI risk register and increasingly a board-level AI governance dashboard.
That dashboard should show where AI is deployed, what business processes and decisions it influences, what data it accesses, where third-party or foundation models are being used and which systems have autonomous capabilities.
“CXOs should report AI adoption and control maturity together,” Mehta says.
The metrics should therefore go beyond the number of AI use cases deployed. Boards should be able to see use cases by risk tier, high-risk systems awaiting approval, incidents and near misses, regulatory exposure, data sensitivity, human-oversight coverage, testing status, third-party dependencies and remediation progress.
For Indian enterprises, that view also needs to account for DPDP obligations, sectoral regulatory expectations, customer complaints, potential algorithmic bias and reputational risk.
The challenge for the board is to convert technical AI risks into business language — financial, operational, regulatory and reputational exposure.
One governance architecture instead of a compliance maze
As enterprises operate across jurisdictions, another risk is emerging: governance fragmentation.
An Indian multinational or a global enterprise with significant operations in India may need to navigate the NIST AI Risk Management Framework, ISO/IEC 42001, DPDP obligations, cybersecurity requirements, sectoral expectations and regulations in overseas markets.
Treating each requirement as a separate compliance programme could create exactly the kind of bureaucracy that AI governance is supposed to prevent.
“The challenge is not a lack of frameworks but the proliferation of overlapping requirements,” Mehta says.
His answer is to establish a single enterprise AI governance and control framework and map external obligations to it.
NIST AI RMF can provide the risk-management logic, while ISO/IEC 42001 provides the discipline of an AI management system. Indian requirements can then be incorporated into the same architecture through controls covering privacy, transparency, documentation, human oversight, data governance, impact assessment and incident reporting.
The operating model should be built around a single AI inventory, a standard risk taxonomy, common workflows and reusable evidence.
This would allow governance to become part of product, data and technology delivery rather than a parallel compliance function.
Governance could become the competitive advantage
The most consequential shift may be that AI governance itself becomes a source of competitive differentiation.
As foundation models become increasingly accessible, access to a particular model is unlikely to remain a sustainable advantage. Two enterprises can use the same underlying technology and still achieve very different outcomes based on how effectively they control, integrate and scale it.
“Two organisations may use the same foundation model, but the one with stronger risk classification, data controls, accountability, monitoring and autonomous-agent oversight is likely to scale faster because it will face fewer incidents, reversals and approval bottlenecks,” Mehta explains.
That turns governance from a defensive function into a form of enterprise infrastructure.
CXOs, therefore, need to build reusable control patterns rather than design governance from scratch for every AI initiative. Low-risk use cases can operate within pre-approved guardrails, while high-impact systems can be subjected to deeper controls and oversight.
Risk, technology, security, legal and business teams also need clearly defined accountability rather than fragmented ownership.
The end goal is not an enterprise where every AI action requires human approval. Nor is it one where autonomous systems operate without meaningful oversight.
It is an enterprise where the degree of autonomy is matched by the degree of control.
“Governance is not a brake on AI adoption; it is the operating system for responsible AI at scale,” Mehta says.
That may ultimately be the defining shift in enterprise AI. The next competitive advantage will not simply belong to organisations that can deploy AI fastest, but to those that can create the architecture, controls and accountability to let AI act at scale — without losing the trust of customers, employees, regulators or the board.
