Why observability must evolve into a system of control


As enterprises move AI agents from experimentation into business-critical workflows, the challenge is shifting from proving that the technology works to establishing whether it can be trusted to operate with autonomy.
For CIOs, this means conventional application and infrastructure monitoring is no longer sufficient. Agentic systems can access data, invoke APIs, make decisions, hand off tasks to other agents and trigger business actions. Understanding whether an agent is behaving as intended requires visibility across this entire chain.
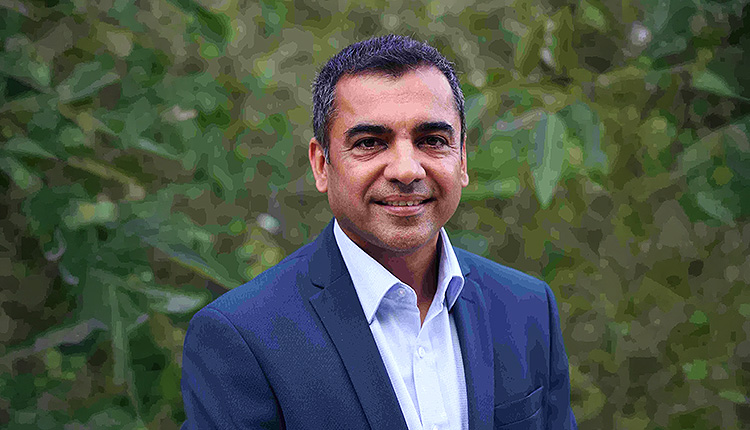
Prashant Chaudhary, Area Vice President, India, Splunk, says the biggest barrier to scaling AI is confidence, which depends on having sufficient operational context.
“Enterprises need to see what their agents are doing, what they cost and whether their actions can be trusted,” he says. “Many organisations can monitor individual applications and infrastructure but cannot trace an agent’s complete journey — what data it accessed, which identity it used, which tools or APIs it called, which other agents it relied on, and what action followed.”
For Indian enterprises operating in sectors such as banking, telecom and public services, these gaps can have direct implications for customer-facing and citizen-facing systems.
From application monitoring to agent observability
Traditional observability focuses largely on whether a service is available, responsive and meeting its service-level objectives. Agent observability must answer a broader question: is the system doing the right thing?
This requires telemetry around an agent’s objective, retrieved context, model behaviour, tool calls, hand-offs, output quality, policy violations and downstream impact.
“Observability must therefore evolve from an engineering dashboard into a discipline that connects technical performance, decision quality, governance and business value,” Chaudhary says.
The distinction becomes particularly important when an AI agent produces an incorrect output or takes an unintended action. Looking only at the model response may obscure the actual cause. The failure could originate in incomplete context, poor-quality data, an unexpected API response, an upstream service failure or another agent passing along an incorrect assumption.
CIOs therefore need a shared record of the interaction that spans the model, data, applications, APIs, infrastructure and identity layers. OpenTelemetry-compliant instrumentation can support this by making applications measurable from the outset, while correlated telemetry can help teams reconstruct the sequence of events rather than investigating isolated logs.
Accountability must be built into autonomy
The ability to reconstruct an agent’s actions also becomes critical when an autonomous system creates financial or operational impact.
An auditable record should capture the agent’s identity, permissions, objective, available data and context, model response, tools and APIs invoked, other agents involved, approvals and eventual business action.
This does not necessarily mean putting a human in the loop for every decision. Instead, autonomy should be proportionate to risk.
“Autonomy should be adjustable: an agent may recommend, request approval or execute, depending on the risk,” Chaudhary says.
Low-risk activities can therefore operate autonomously, while higher-impact actions can trigger approval, policy enforcement or runtime intervention. The objective is to make autonomy governed and reviewable rather than eliminating it.
This also requires enterprises to treat AI agents as a new class of digital worker, with a defined identity, bounded permissions and clear ownership.
Cost and resilience become part of observability
As agent deployments scale, CIOs will also have to connect technical performance with economics. Token consumption, inference costs, latency and output quality need to be evaluated alongside business outcomes.
The same visibility must extend across private, on-premises and air-gapped environments, particularly for organisations with stringent data-residency or regulatory requirements.
Chaudhary recommends that enterprises establish visibility and baseline measures for behaviour, security and cost before expanding agent autonomy.
“Organisations should expand agent autonomy only as their ability to observe, control and account for its actions improves,” he says.
Building the foundation before scaling
Over the next 12–18 months, the priorities for CIOs are likely to centre on five connected capabilities: an inventory of AI agents and their accountable owners; machine-orientated identity and access controls; AI observability covering behaviour, security, quality and cost; a governed data foundation; and an operating model combining policy-defined autonomy, human oversight, auditability and incident-response playbooks.
The sequencing is critical. Enterprises need to understand what agents are doing before they allow them to do more.
Data from Splunk’s CISO Report 2026 underscores the gap. The report says 96% of global CISOs oversee AI governance and risk across the enterprise, while 41% say they cannot correlate ROI to risk mitigation and remediation activities. In India, 75.7% of respondents are not currently using agentic AI, with 21.4% in early exploration.
It offers companies an opportunity to govern, observe and become accountable for their actions even before these agents are fully integrated into business processes.
The next step in AI enterprise may not be about how much autonomy organisations can give these agents, but rather about how comfortable they are in observing, controlling and accounting for their actions.
