In the agentic era, identity and intent become the new pillars of enterprise security


As enterprises move deeper into the AI era, the traditional security model built primarily around human users is beginning to face a fundamental challenge. AI agents are no longer simply assisting employees with tasks. They are increasingly interacting with enterprise data, applications and APIs, making decisions and taking actions autonomously.
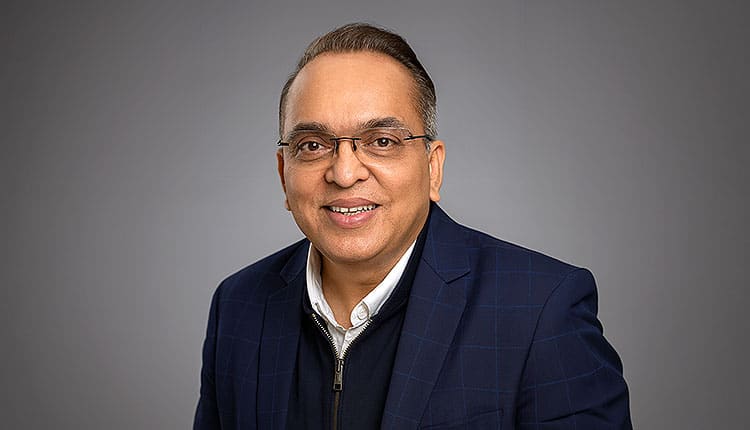
According to Ninad Katkar, Leader, Security, Cisco India & South Asia, this does not mean abandoning user-centric security but extending the architecture to account for a new class of digital actors. “AI agents are becoming a new class of the digital workforce. These agents basically hold identities, they access applications, they keep on making API calls, and they do the data interactions also. And they also interact with other agents, which is a very fundamental and unique thing about the agents.”
The defining challenge, he says, is the speed at which these systems operate. Unlike human users, agents can execute actions at machine speed, potentially amplifying both productivity and risk.
This is driving a shift towards what Katkar describes as an identity- and intent-centric security architecture.
Moving beyond human-centric security
In a traditional security environment, establishing a user’s identity and determining their role typically forms the basis for authorisation. With autonomous agents, however, knowing who or what an agent is becomes only the starting point.
“Every agent should answer five questions. What is this agent all about? What is it allowed to do? Why and what is it trying to do? So, what data and tools is it accessing? And can we stop that access immediately?”
Identity, therefore, needs to be accompanied by continuous verification of intent.
Katkar illustrates the issue through a simple example. An organisation may deploy an agent capable of accessing a database and generating reports. If the agent is compromised or behaves maliciously, however, it could potentially move beyond its intended task and access information it was never supposed to retrieve. “If I want to see my salary slips, and instead of that, the agent works autonomously and gives me the salary slips of my peers. That’s dangerous,” he says.
The concern is not necessarily that the underlying system lacks security controls, but that an autonomous agent can operate differently from what it was originally authorised to do.
This makes continuous verification of both identity and intent critical.
The identity problem enterprises need to solve first
Before organisations can secure AI agents, Katkar argues, they need to know which agents actually exist within their environments and whether those agents have an identity.
Agents can take multiple forms—end-user agents, SaaS application agents or third-party agents—and enterprises may already have agents operating without clear ownership or identity.
“Don’t be surprised, most organisations are already struggling with this problem because there will be a lot of agents in the organisation which might not have an identity. It means that nobody would have an idea of who is using this agent, who is authorising this agent, and what kind of authority has been given to this agent.”
An agent without an identity becomes particularly difficult to govern because there is no clear mechanism for controlling its authority or tracing its actions.
Katkar’s approach is straightforward: organisations need to establish whether an agent has an identity. If it does not, enterprises should either assign one or stop its access.
Once identity is established, the next step is determining what authority the agent should receive.
That authority, he says, should always follow the principle of least privilege. An agent created to retrieve an employee’s payslip should have access only to the information necessary for that task, not the wider database.
“Continuous authorisation of the identity is required,” he says. “We have to make sure that we give the least privilege access.”
Security and networking can no longer operate in isolation
The emergence of AI agents is also accelerating the convergence between networking and security.
Historically, organisations often treated security as a separate layer over the network. That model became increasingly difficult as employees moved from corporate offices to branches, homes and other locations. “You can’t have security based on the location. You can’t have security as a bolt-on over the network. So, this means that you have to make sure that security is embedded into the network.”
For Katkar, this principle becomes even more important in an agentic environment, where the source of an interaction may no longer be a human user sitting at a particular location.
Security and networking teams therefore need to work together from the architecture stage, considering where users operate, where workloads reside and how applications and agents interact.
The objective is to establish enforcement points based on identity, source, destination and context rather than relying on physical network boundaries.
Zero Trust needs to account for agents
This shift also changes the way enterprises approach Zero Trust.
Traditional Zero Trust principles are based on eliminating implicit trust and continuously verifying access. But Katkar points out that these principles were largely designed around human users.
“If I have one or two agents, which is going to be a norm for most of these enterprises, what will happen is that not only do I have to design the Zero Trust for Ninad as an individual, as a human, but I also have to design the Zero Trust for the two or three agents which are designed for Ninad.”
Creating entirely separate Zero Trust architectures for humans and agents, however, could introduce additional complexity.
Instead, he argues for a unified model that accounts for human identities, agent identities and workloads. “Now they have to fundamentally think about one Zero Trust system which is meant for both agent and human workloads and identity also.”
Securing AI itself
The security challenge also extends beyond protecting agents and their access. Enterprises need to secure the AI systems themselves.
Katkar distinguishes between AI for security and security for AI. “AI for security helps defenders to become faster and more effective. But security for AI addresses a very fundamental question, which is, can the enterprise trust the AI system now making decisions and taking the actions?”
That requires security controls across the entire AI lifecycle.
The process begins with data: understanding where it originates, whether it has been manipulated and whether sensitive information is entering an unauthorised model.
Security then needs to extend to models and applications, including questions around whether the model is legitimate, vulnerable to tampering, producing unsafe outputs or exposed to supply-chain compromise.
Runtime security becomes another critical layer.
“Every prompt and response” needs to be inspected, Katkar says, so enterprises can identify prompt injection, data leakage, harmful content or policy violations.
The fundamental questions remain centred on identity and intent: Is the agent approved? What is its intended purpose? Which data, tools and systems can it access? Are its permissions limited to what it actually needs? And are its actions consistent with its approved intent?
Controlling privilege creep
As enterprises deploy multiple agents for different tasks, preventing privilege creep becomes another critical concern.
Katkar describes a scenario where an employee may have one agent helping with software development, another retrieving reports from a database and another managing travel.
Each agent should have a specific identity and a clearly defined task. The authority granted to the agent should correspond only to that task.
“Any deviation from them should be highlighted, and hence observability becomes a very critical part,” he says.
There also needs to be an enforcement mechanism capable of stopping an agent if it crosses its authority boundaries.
This makes observability a core security capability rather than an afterthought.
Designing for an AI-native enterprise
Looking ahead, Katkar believes security architecture itself needs to be redesigned around the assumption that non-human actors will eventually outnumber human users.
“If I get a chance to design AI-native enterprises from scratch, I would begin with an assumption that in this particular organisation there will be more non-human actors, I would say, than the human users.”
His approach is to move away from security as a collection of controls attached to fixed locations and towards a distributed trust architecture built around identities, data, interactions and actions.
He outlines five principles: every human, device, workload, application and AI agent should have a unique, verifiable identity; access should be temporary, least-privileged and intent-based; security enforcement should operate across networks, cloud, applications and AI rather than being tied to a location; AI systems should be tested before production and continuously inspected; and observability and response should operate at machine speed.
The final principle may prove particularly important as enterprises deploy increasingly autonomous systems.
“Unlike humans, agents will act at a machine speed,” Katkar says. “The enterprise must be able to detect abnormal behaviour and revoke the access in seconds, not after the multiple investigations.”
Today, security is about understanding which identity is acting, what it intends to do, what authority it has, and whether its actions remain within that intent. As AI moves from assisting users to acting on their behalf, those distinctions are becoming central to how enterprises will build trust into their next generation of digital infrastructure.
