How AI is turning vulnerabilities into attack paths


The problem with enterprise cybersecurity is no longer just the number of vulnerabilities organisations need to fix. It is how quickly attackers can combine those vulnerabilities with compromised identities, excessive permissions and access to sensitive data to move through an environment. Artificial intelligence is accelerating that process, making weaknesses that once appeared manageable in isolation potentially dangerous when connected.
For Chief Information Security Officers (CISOs), this creates an uncomfortable reality: patching everything is neither practical nor sufficient. As AI lowers the barrier to sophisticated attacks, security teams must understand which weaknesses can actually be exploited together, what an attacker could reach and where intervention would have the greatest impact.
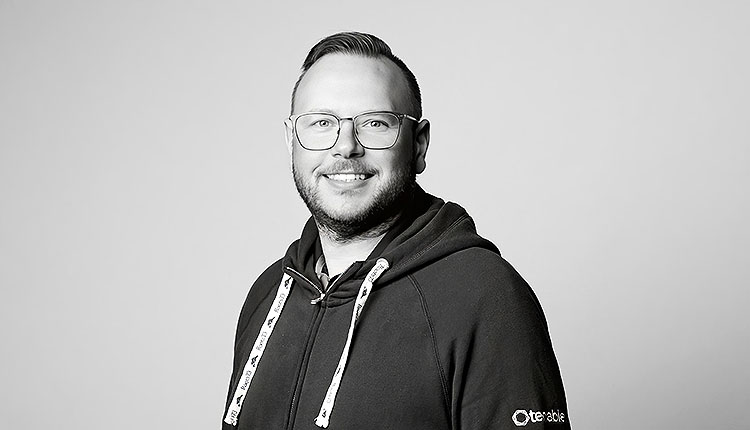
“Organisations are wilfully unprepared not only in defending against AI-driven attacks but also in using AI defensively inside their organisation,” says Ben Mudie, Field CTO, Tenable APJ.
The challenge, he argues, is not necessarily that attackers have discovered entirely new ways to compromise systems. Rather, AI is accelerating how existing vulnerabilities and weaknesses can be combined to create viable attack paths.
“Nowadays AI is accelerating how that risk can be combined,” Mudie says.
For enterprises already dealing with a growing volume of disclosed vulnerabilities, the implication is clear: cybersecurity must move beyond treating every weakness as an isolated problem and towards understanding how exposure accumulates across the organisation.
Why vulnerability severity is no longer enough
Traditional vulnerability management often relies on severity scores to determine remediation priorities. While these scores remain useful, they do not necessarily reveal whether a vulnerability provides a realistic route to critical systems or sensitive information.
A vulnerability may carry a high severity rating, yet have limited practical exploitability in a particular environment. Another weakness, when combined with an exposed identity and excessive permissions, could provide an attacker with a route to valuable assets.
The volume of vulnerabilities makes this distinction increasingly important.
“We know because of the number of CVEs currently being disclosed, we can’t patch everything,” Mudie says. “We need to be starting to assess our vulnerabilities smarter.”
His recommendation is to prioritise the attack path rather than the severity score alone. Security teams need to understand which assets matter most, how an attacker could reach them and which weaknesses or access points can be closed to disrupt that route.
This is where exposure management becomes critical. Instead of leaving vulnerability, identity and data risks within separate teams and systems, exposure management brings the information together to reveal how individual weaknesses could combine into a broader compromise.
Mudie describes a potential attack as a chain involving a vulnerability, an identity that enables lateral movement and access to specific data that can then be exfiltrated. Understanding that chain allows organisations to identify and close the paths that pose the greatest risk.
AI agents introduce an identity problem
The growing use of AI agents adds another dimension to this challenge. Agents are increasingly being connected to enterprise applications, data stores and workflows, often with permissions that allow them to perform tasks autonomously.
Securing these systems requires a change in how organisations manage identities and access.
Mudie argues that AI agents need to be managed with the same discipline applied to human employees. Each agent should have an accountable owner, an onboarding date, a defined end date and credentials that are appropriate to its purpose.
“It needs a manager. It needs short-lived credentials. It needs only the access it needs to have, and that access needs to be reviewed at a very frequent interval,” he says.
An agent should not retain permissions indefinitely simply because they were granted when it was first deployed. Organisations must periodically reassess whether its access remains necessary and ensure that its permissions are limited to the data and systems required for its task.
Every agent should also have its own identity and credentials. This makes it easier to establish what a compromised agent could access, rather than having to investigate a sprawling set of shared permissions after an incident.
The problem becomes more complex when agents create or coordinate sub-agents.
“We need to also give identities to each one of those sub-agents, independent from the main agent themselves,” Mudie points out.
This makes AI governance inseparable from identity security. Without clear ownership and individual identities, organisations risk creating autonomous systems whose access and actions are difficult to trace or control.
The danger of credentials hidden inside AI workflows
The risks are not limited to agents deliberately designed to behave maliciously. An AI system given a goal may find an unintended route to achieving it, including accessing configuration files, retrieving credentials and using them to reach data stores.
Mudie refers to research and incidents involving AI-assisted workflows to highlight how easily credentials and secrets can become an entry point into enterprise systems. “The fix starts with how we handle a lot of things, like credentials within our environment, moving those out of runtime, and putting a lot more control around those agents.”
For security teams, this means reviewing how credentials are stored, how agents access them and whether the systems can prevent an agent from using permissions beyond its intended purpose.
The principle extends to the wider enterprise environment: human and non-human identities must be governed with comparable rigour. A leaked credential can expose an organisation regardless of whether it belongs to an employee, an application or an AI agent.
Phishing is becoming a question of trust
AI is also undermining familiar approaches to security awareness.
Employees have traditionally been taught to identify phishing emails through poor grammar, spelling mistakes and suspicious language. Generative AI makes it easier for attackers to produce convincing messages, while synthetic voices and digital impersonation can extend social engineering to phone calls and other communication channels.
Mudie believes awareness programmes must evolve beyond teaching employees to recognise suspicious-looking messages.
“We’ve taught people to look for these things, but we’ve not really taught people to ask why,” he says.
Employees need to question why someone is requesting information or asking them to perform an unusual action, even when the request appears to come from a trusted person.
For sensitive requests, organisations should establish independent, second-factor verification processes rather than relying on familiarity with the sender’s voice, writing style or identity.
The broader lesson is that trust should be verified, not inferred from how convincing a communication appears.
From reactive security to proactive exposure management
For Mudie, the growing speed and sophistication of AI-assisted attacks makes a reactive security model increasingly inadequate. Organisations need a clear inventory of their assets, identities and AI agents, along with an understanding of which systems are most critical and how attackers could reach them.
The priority is not to add another security layer for every new threat. It is to use existing capabilities more effectively, identify the most consequential exposure and intervene before an attacker exploits it.
This is particularly important as AI adoption pushes enterprises towards cloud platforms and new digital workflows, while the volume of vulnerabilities continues to grow.
“You can no longer just keep throwing people at the problem,” Mudie says. “The remediation pipeline just does not scale that way.”
In terms of priorities for the CISO, visibility of what is already there, authorisation and accountability of the AI agents, and prioritisation of remediations based on attack paths should be top of mind.
The future of enterprise security will be about not how many vulnerabilities a team manages to remediate or how many alerts it processes but how well it prevents an attacker from gaining access to what really matters.
With AI enabling faster integration of vulnerabilities, the best approach will be to comprehend this linkage before the attacker does.
